
What a cybersecurity risk assessment is, in plain English
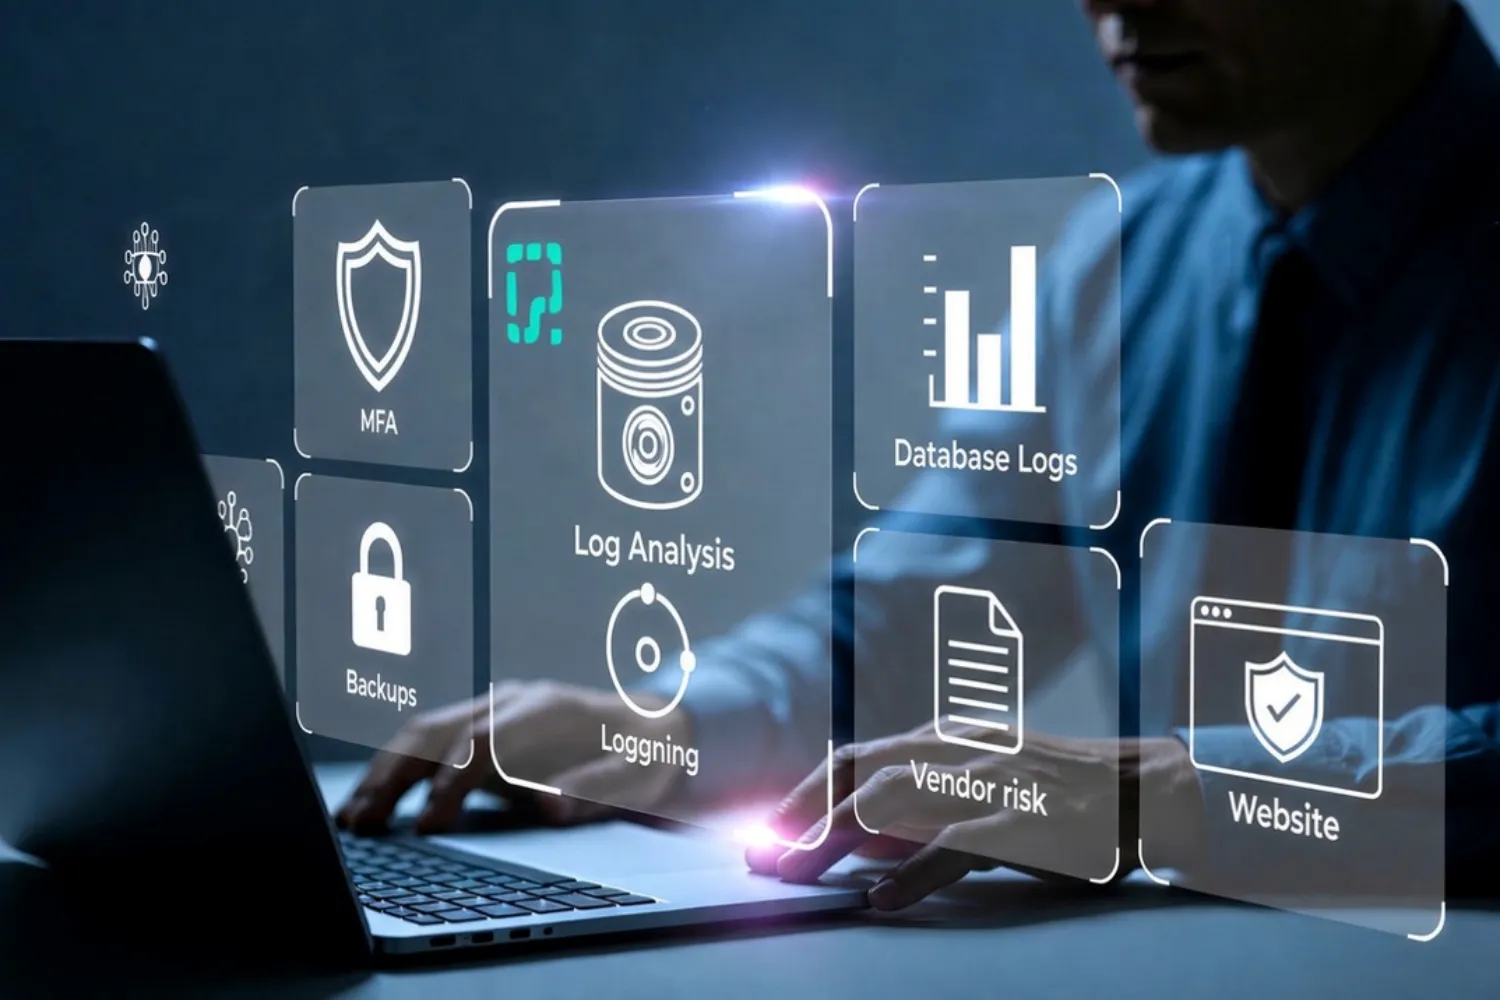
A cybersecurity risk assessment is a structured review of where your business is exposed, what could go wrong, and which gaps matter most. For a small business, that usually means looking at access controls, backups, software updates, vendor access, email security, cloud apps, and any public-facing systems like your website.
Federal guidance for small businesses consistently points to the same basics: identify risks, use multi-factor authentication, back up important data, keep systems patched, review supplier risk, and keep enough logging to investigate issues if something happens. The Federal Trade Commission, the Cybersecurity and Infrastructure Security Agency, and the Small Business Administration all emphasize those fundamentals in their small-business cybersecurity guidance.
What to review before the assessment
If you are planning a professional cybersecurity risk assessment, it helps to do a quick internal review first. That does not replace a full assessment, but it gives you a clearer starting point and makes the final review more useful.
1. Confirm who has access to what
Start by reviewing administrative accounts, shared logins, former employee access, and third-party tools. Make sure you know who can access important systems such as email, payroll, banking, file storage, and your website. Look for accounts that are shared by multiple people, access that still belongs to former employees, and vendors that may have more permissions than they actually need.
If you cannot produce a clean list of users and their privileges, that is often one of the first issues a cybersecurity risk assessment should uncover.
2. Check your MFA coverage
Multi-factor authentication adds a second verification step when someone signs in and is one of the most practical ways to reduce the risk of account takeover.
Before the assessment, confirm that multi-factor authentication is enabled anywhere sensitive information or important business systems can be accessed. This should include email, cloud storage, accounting and payroll systems, remote access tools, your WordPress administrative area, and other systems that contain confidential or business-critical data.
A professional assessor will usually want to know not only whether multi-factor authentication is available, but whether it is consistently enabled everywhere it should be.
3. Review backups and recovery
Backups are only useful if they can be restored successfully. Before a risk assessment, make sure you understand what is being backed up, how frequently backups run, where the backup copies are stored, and whether those copies are protected from normal user access.
You should also know when a restore was last tested. Many businesses discover that backups have been running for years without anyone actually verifying that the data can be recovered. It is better to discover that problem during an assessment than during an emergency.
4. Look at software updates and old systems
Outdated software and unsupported systems can create unnecessary security exposure. Review the computers and laptops used by the business, any servers you operate, network equipment, and the software employees depend on.
For a WordPress website, this also means checking WordPress itself, installed themes, and plugins. Browser extensions and locally installed applications that handle business information should also be considered.
If you find systems that are no longer supported, are rarely updated, or have unclear ownership, flag them for further review during the assessment.
5. Inventory vendors and cloud apps
Third-party services are an important part of modern cybersecurity risk management. Even a small business may depend on a large number of outside providers for technology and business operations.
Identify the companies and services that support your business, including information technology providers, website hosting companies, email providers, customer relationship management and marketing platforms, file-sharing services, payment processors, and subcontractors that handle client or employee information.
You do not need to complete a detailed contract review before the assessment. The important first step is knowing which vendors hold your data, who administers those accounts, and what impact a compromised vendor account could have on your business.
6. Check logging and alerting
Logging provides a record of activity on your systems and can help identify suspicious behavior, unauthorized changes, and other security problems.
Before the assessment, determine whether administrative activity is being recorded for important systems such as email, website hosting, and cloud services. Check whether alerts are enabled for events such as unusual logins or permission changes, and determine whether someone is actually responsible for reviewing those alerts.
A cybersecurity risk assessment is much more useful when there is enough logging available to verify what happened rather than trying to reconstruct events after the fact.
7. Review your website and web apps
For many small businesses, the website is more than a simple online brochure. It may collect leads, process forms, accept file uploads, connect to payment systems, or exchange information with email marketing and customer relationship management platforms.
Because of that, the website should be included as part of the cybersecurity risk assessment. Review WordPress and plugin updates, contact forms, file upload settings, administrative accounts, secure website connections, basic site security settings, and any third-party scripts or services that have been added to the site.
It is also important to consider whether the website collects or exposes more information than is necessary. If the website supports normal business operations or handles customer data, it belongs inside the overall cybersecurity assessment rather than being treated as a completely separate system.
A simple checklist you can use today
If you want a quick internal pass before scheduling a professional review, use this as a starting point:
- MFA is enabled on critical accounts
- Former employees no longer have access
- Backups exist and have been tested
- Key systems are up to date
- Vendors and cloud apps are documented
- Admin access is limited
- Logs and alerts are being reviewed
- Website forms, plugins, and integrations are current
- Sensitive data is stored only where it needs to be
If several of those items are unclear, that is a sign the assessment will need to focus on discovery first.
Where AI and website tools fit in
If your business uses AI tools, chat features, or AI-assisted website services, add them to the review. The SBA advises small businesses to use AI carefully and review the benefits and risks. NIST also emphasizes testing, evaluation, verification, validation, and documented risk management for AI-related systems.
For most businesses, the practical questions are simple:
- What data does the tool collect?
- Who can see that data?
- Is any customer or employee information being sent to a third party?
- Does the tool create new access or privacy exposure on your site?
- Can search engines and AI systems crawl the public content you want them to see?
That last point matters for visibility too. Public, crawlable content supports both traditional search and broader AI discovery, but only when the site is set up cleanly and the content is technically accessible.
When outsourcing makes sense
If your team is small, a cybersecurity risk assessment can be hard to do well from the inside. You may know the business process, but not have enough time to inspect access, backups, logs, website settings, and vendor exposure in a structured way.
That is where outside help can be useful. A good assessment should leave you with a clearer picture of what is exposed, what is already working, and what needs attention first.
At Solutions by BG, we help businesses review practical technical risk across systems, websites, and day-to-day operations so they can make informed decisions without building a large internal IT team.
Next step
If you want a better sense of your website’s technical condition and how it fits into your broader risk picture, request a Free Website Review.